ISO 27001:2022
Apply for ISO 27001 online.
ISO 27001:2022 Information Security Management
Your customers ask about information security? Assess how your company protects sensitive information. You complete the self-assessment online, with no on-site audit. A member of the SICE Certification Board reviews your answers before the certificate is issued.
CHF 849 in the first year, then CHF 569 per year with an online re-audit.
Pricing- Questions
- 48
- Must-meet questions
- all 13
- Other questions
- min. 24 of 35
- Validity
- 3 years
- First-year price
- CHF 849
- From year 2
- CHF 569 per year
- Assessment time
- about 30 minutes
- Certificate after payment
- usually within 4 h
- Official standard
- iso.org
01: Overview
What is ISO 27001?
ISO 27001:2022 sets out how an information security management system (ISMS) is built. At its core is the risk assessment: it decides which Annex A controls you implement and why. The 2022 edition revised the controls, covering cloud services, data protection and cyber risks among others.
02: Benefits
What ISO 27001 brings your business
The benefits of the standard come from an effectively implemented management system, not from the certificate alone. The Zertify certificate documents your reviewed answers.
- Documented answers in customer security questionnaires
- Fewer security incidents when risks are assessed and treated
- A structure for GDPR and NIS2 requirements
- Answers to many questions when banks, insurers or corporations review their suppliers
- An argument in proposals to security-conscious customers
- A set procedure when an incident happens
03: Who it is for
Who is ISO 27001 for?
- IT service providers and software companies
- Cloud service providers
- Financial service providers and banks
- Healthcare
- E-commerce and online services
- Companies handling sensitive customer data
04: Requirements
Key requirements
Assess information security risks
Define a security policy and objectives
Implement security controls (Annex A)
Prepare a Statement of Applicability (SoA)
Raise awareness and train employees
Manage security incidents and learn from them
05: Demand
Who asks for ISO 27001?
ISO 27001 is what customers with a security questionnaire ask about most often. It usually comes up shortly before the contract is signed.
- Corporate customers in procurement
- Banks, insurers and corporations vet service providers that process their data with a security questionnaire. With an ISMS in place you can answer many of these questions.
- Software and SaaS
- Cloud software vendors are asked about ISO 27001 and encryption early in contract talks. Without an answer, deals stall.
- Regulated industries and tenders
- Healthcare, finance and the public sector require proof of information security, partly by contract, partly through supervision and tender documents.
06: Assessment
How the assessment works
The assessment has 48 yes/no questions, online and at your own pace. 13 of them are must-meet questions of our assessment and must all be answered yes. Of the other 35 questions you need at least 24 yes.
| The questions fall into these topics: | Questions | Mandatory |
|---|---|---|
| Context of the organization | 4 questions | 1 |
| Leadership | 5 questions | 1 |
| Planning | 7 questions | 4 |
| Support | 6 questions | 2 |
| Operation | 5 questions | 2 |
| Performance evaluation | 3 questions | 2 |
| Improvement | 3 questions | 1 |
| Annex A: Organizational controls | 4 questions | 0 |
| Annex A: People controls | 2 questions | 0 |
| Annex A: Physical controls | 2 questions | 0 |
| Annex A: Technological controls | 7 questions | 0 |
After the assessment, a member of the SICE Certification Board reviews your answers. Only then does Zertify issue the certificate.
07: Sample questions
Sample questions from the ISO 27001 assessment
Four of 48 questions from the catalogue, and why they count.
Is an information security risk assessment carried out?
The risk assessment decides which measures you need. Without it every security measure is guesswork and its selection cannot be justified.
Is there a Statement of Applicability (SoA)?
The SoA links risks to measures and is the first document auditors and customers want to see.
Are employees aware of information security?
Most incidents start with people, for example through phishing. What is asked for is training with evidence, not just a policy on the intranet.
Are nonconformities and security incidents addressed?
Incidents cannot be ruled out. What matters is whether you detect, report and assess them and learn from them.
08: What you get
Certificate, badge, verification page and evaluation
What you receive after passing the assessment, and what you use it for.
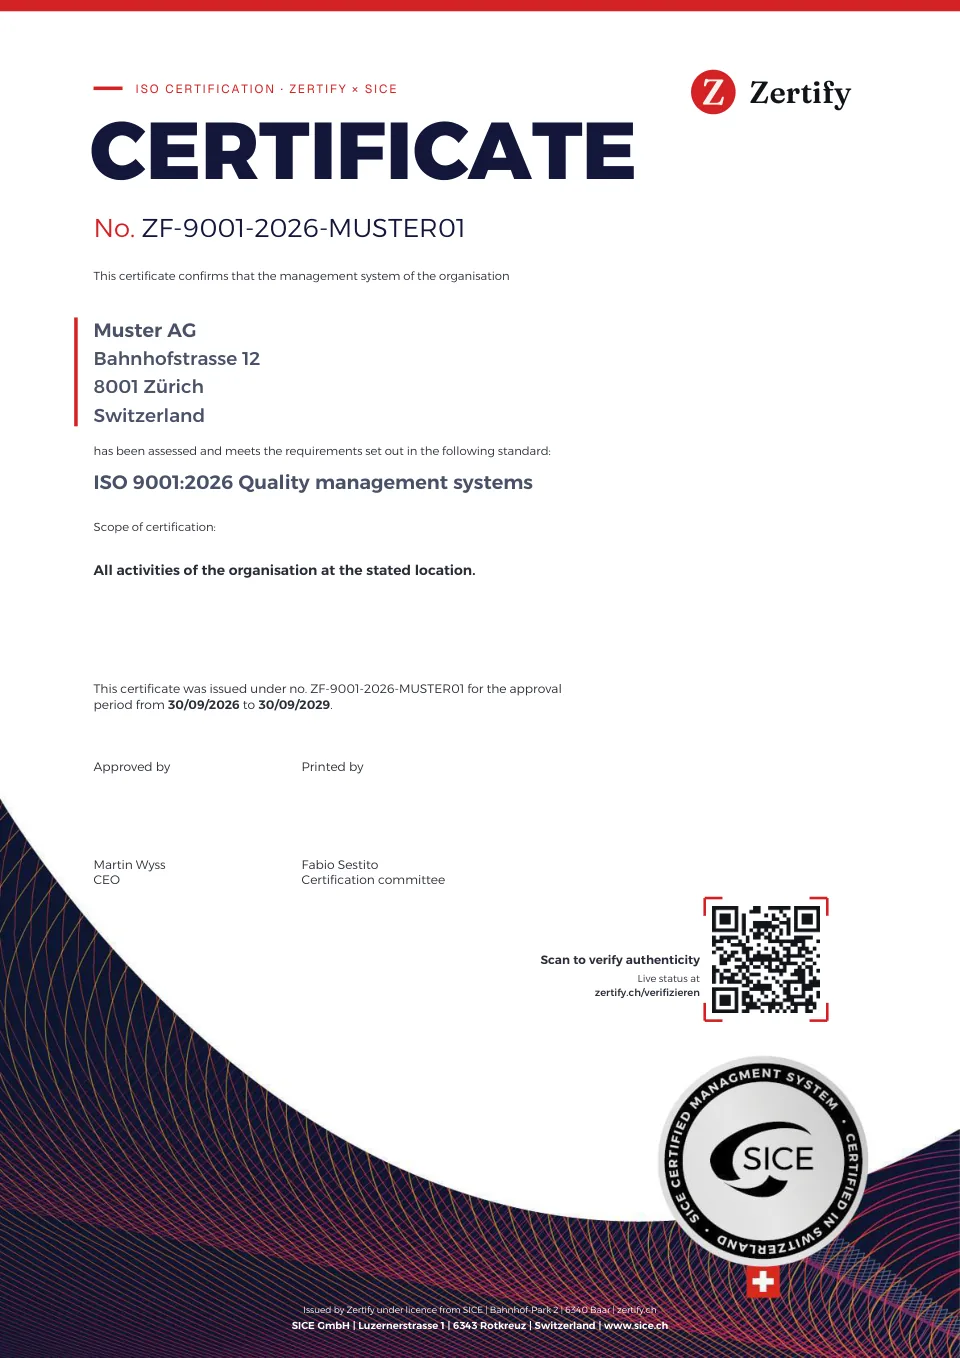
- Certificate as PDFWith number, QR code and the SICE seal. Valid for three years, confirmed by the yearly online re-audit. For customer enquiries, offers and supplier questionnaires.
- Badge for website and documentsFor your website, offers and email signature. One click leads to the verification page; on the website it always shows the current status.
- Public verification pageBy number or QR code, customers see for themselves which company and standard the certificate covers and whether it is valid.
- Evaluation of your assessmentShows which requirements you meet according to your answers and where you should improve.
- Customer accountCertificates, invoices, re-audit and add-ons in one place.
For ISO 27001, the certificate also shows the version of your Statement of Applicability (SoA). An SoA template is available as an add-on.
09: Price
Price and validity
First-year price
CHF 849
- From year 2
- CHF 569 per year
- Validity
- 3 years
Your customer requires an audit or an accredited certification? Clarify requirements
Included in the price
- Online assessment with 48 questions
- Certificate as PDF, issued under licence from SICE
- Yearly online re-audit
- Support by email
The verification page shows the status, standard and validity of every certificate. Read more in the FAQ
See the sample and assessment methodVoices
Customers with ISO 27001
“Our clients give us access to their systems. Before they do, they want to see that we take information security seriously. The ISO 27001 certificate with its Statement of Applicability answers that question, and the QR code makes it verifiable instantly.”
Michael Popsor, Managing Director
Sopranos IT Solutions LLC
ISO 27001:2022Check certificate
10: Cost
What does ISO 27001 cost? Audit, consulting or self-assessment
ISO 27001 takes more effort than quality or environment, because an ISMS with risk analysis and policies has to be built. For 10 to 50 employees, these orders of magnitude apply.
| Route | Indicative range | What is behind it |
|---|---|---|
| Accredited audit | Indicative rangeCHF 8,000 to 20,000 initial audit, then 4,000 to 8,000 per year | What is behind itAudit days grow with headcount, sites and the scope of the ISMS. A scope limited to one product line is much cheaper than the whole company. |
| Consulting and implementation | Indicative rangeCHF 15,000 to 50,000 one-off | What is behind itRisk analysis, statement of applicability, policies and training are built externally. Technically strong teams save the most here. |
| Zertify self-assessment | Indicative rangeCHF 849 in year 1, then CHF 569 per year | What is behind itYou check whether risk analysis, statement of applicability, policies, training and incident management are demonstrably in place. It replaces neither a penetration test nor an audit. |
All amounts are non-binding indicative ranges for Swiss SMEs, not quotes. The offers of the individual providers are what counts.
11: Duration
How long does ISO 27001 take?
An accredited ISMS is rarely ready in under six months, usually it takes nine to twelve. The time goes into the build, not the audit.
| Phase | Accredited | Zertify |
|---|---|---|
| Build the ISMS | Accredited6 to 12 months for scope, risk analysis, SoA, policies and training | ZertifyNone. You rate the current state of your information security |
| External audit | AccreditedStage 1 (documents) and stage 2 (implementation), plus 4 to 8 weeks of lead time | ZertifyAbout 20 to 30 minutes online, scored immediately |
| Certificate | AccreditedRelease after 2 to 6 weeks, annual surveillance audits, recertification after three years | ZertifyPDF with QR verification within 4 hours |
12: Further questions
Further questions about ISO 27001
Questions
Industries
- ISO 27001 for IT companies
- ISO 27001 for healthcare
- ISO 27001 for manufacturing
- ISO 27001 for logistics
- ISO 27001 for retail and trade
- ISO 27001 for service companies
- ISO 27001 for chemicals and pharma
- ISO 27001 for financial services
- ISO 27001 for real estate
- ISO 27001 for energy sector
- ISO 27001 for education
RegionsShow regionsHide regions
- ISO 27001 in Zurich
- ISO 27001 in Bern
- ISO 27001 in Basel
- ISO 27001 in Geneva
- ISO 27001 in Lausanne
- ISO 27001 in Lucerne
- ISO 27001 in St. Gallen
- ISO 27001 in Zug
- ISO 27001 in Winterthur
- ISO 27001 in Lugano
- ISO 27001 in Aarau
- ISO 27001 in Schaffhausen
- ISO 27001 in Chur
- ISO 27001 in Fribourg
- ISO 27001 in Neuchâtel
- ISO 27001 in Biel
- ISO 27001 in Thun
- ISO 27001 in Solothurn
- ISO 27001 in Sion
- ISO 27001 in Frauenfeld
Checklist
ISO 27001:2022 checklist by email
All 48 questions of the ISO 27001 self-assessment as a PDF to tick off, ordered by topic. Free, by email.
13: More standards
More standards
Many companies combine several standards. Two or more earn a discount.
- ISO 27017:2015: View standard
Cloud Security
If you run or use cloud services, you extend your ISMS with the cloud controls and settle responsibility between provider and customer.
from CHF 799
- ISO 27018:2025: View standard
Cloud Privacy
If you process personal data for customers in the cloud, ISO 27018 covers data protection on top of the ISMS.
from CHF 799
- ISO 20000-1:2018: View standard
IT Service Management
IT service providers combine security with service quality. Incident and change processes are anchored in both standards.
from CHF 799
14: Blog
Latest articles on ISO 27001
15: Questions
Frequently asked questions about ISO 27001
Yes. The Statement of Applicability is mandatory. It lists all Annex A controls, says whether they apply and whether they are implemented, and justifies every exclusion. Without an SoA you will not pass an audit.
Annex A shrank from 114 to 93 controls in four themes: organisational, people, physical and technological. Eleven controls are new, including threat intelligence, cloud services and data deletion. The transition period for the 2013 version has ended.
No. Technology is only one part. The standard requires a management system: assess risks, justify measures, name owners, measure effectiveness and improve regularly.
ISO 27001 sets the requirements for the management system and is certifiable. ISO 27002 is a guideline that explains the Annex A controls and gives implementation advice. In practice you work with both.
Yes, with a narrow scope. A small team has fewer systems, short paths and needs fewer policies. Set the scope on the product customers care about and widen it later.
For proposals, supplier questionnaires, many tenders and internal use. It shows that you answered the requirements of the standard in the online assessment and that a member of the SICE Certification Board reviewed your answers. If a tender explicitly requires an accredited certificate, check this first via the Clarify requirements page.
ISO 27001 certificate within 4 hours.
The assessment is free. You pay only once you have passed.
The verification page shows the status, standard and validity of every certificate.