ISO 27017:2015
Apply for ISO 27017 online.
ISO 27017:2015 Cloud Security
Assess the security controls and responsibilities in your cloud environment. You complete the self-assessment online, with no on-site audit. A member of the SICE Certification Board reviews your answers before the certificate is issued.
ISO 27017 is certified together with ISO 27001. ISO 27001 is included in the assessment automatically.
Start the ISO 27017 assessmentPackage with ISO 27001: CHF 1'318.40 in the first year, then CHF 878.40 per year with an online re-audit.
Pricing- Questions
- 34
- Must-meet questions
- all 12
- Other questions
- min. 15 of 22
- Validity
- 3 years
- First-year price, ISO 27017 alone
- CHF 799
- Package with ISO 27001
- CHF 1'318.40
- Assessment time
- about 30 minutes
- Certificate after payment
- usually within 4 h
- Official standard
- iso.org
01: Overview
What is ISO 27017?
ISO 27017:2015 is a code of practice with security controls for cloud services. It extends ISO 27001 and ISO 27002 and addresses cloud providers and cloud customers alike. The central question is who handles which security task, from tenant segregation and administrator access to data return.
02: Benefits
What ISO 27017 brings your business
The benefits of the standard come from an effectively implemented management system, not from the certificate alone. The Zertify certificate documents your reviewed answers.
- A written split of what the provider secures and what the customer secures
- Controls for tenant segregation, hardening and administrator access
- Extends an existing ISO 27001 ISMS
- Answers to the cloud questions in security questionnaires
- Lower risk when outsourcing to the cloud
- Clear rules for data return and deletion at contract end
03: Who it is for
Who is ISO 27017 for?
- Cloud service providers (IaaS, PaaS, SaaS)
- Companies that use cloud services
- IT service providers with cloud offerings
- Data centres and hosting providers
- Software companies with cloud solutions
- Managed service providers
04: Requirements
Key requirements
Carry out a cloud-specific risk analysis
Define responsibilities clearly (shared responsibility)
Ensure data isolation and tenant segregation
Guarantee secure deletion of customer data
Implement virtualisation security
Establish cloud-specific incident response
05: Demand
Who asks for ISO 27017?
ISO 27017 is asked for where data moves to the cloud and customers want to know who is responsible for which security.
- Customers of cloud providers
- Companies that buy SaaS or hosting check the provider for tenant separation, administrator access and return of data.
- SaaS and hosting providers
- Anyone who sells cloud services is asked about ISO 27017 alongside ISO 27001 in security questionnaires, because it describes the cloud controls.
- Regulated industries
- Finance and healthcare demand a traceable split of responsibility and control over the provider when they outsource to the cloud.
06: Assessment
How the assessment works
The assessment has 34 yes/no questions, online and at your own pace. 12 of them are must-meet questions of our assessment and must all be answered yes. Of the other 22 questions you need at least 15 yes.
| The questions fall into these topics: | Questions | Mandatory |
|---|---|---|
| Shared responsibilities | 5 questions | 3 |
| Asset management and data return | 5 questions | 2 |
| Tenant segregation and isolation | 5 questions | 1 |
| Virtual machines and hardening | 4 questions | 1 |
| Administrator access and privilege management | 5 questions | 2 |
| Cloud monitoring and logging | 5 questions | 1 |
| Network security in the cloud | 3 questions | 1 |
| Incident response in the cloud | 2 questions | 1 |
After the assessment, a member of the SICE Certification Board reviews your answers. Only then does Zertify issue the certificate.
07: Sample questions
Sample questions from the ISO 27017 assessment
Four of 34 questions from the catalogue, and why they count.
Is the division of tasks between your company and the cloud provider documented in writing in a shared responsibility model?
Without a written split of duties, each side assumes the other secures something. This model is the core of the standard.
Is it contractually agreed that the cloud provider returns or verifiably deletes all customer data at the end of the contract?
On termination the contract decides whether your data comes back and when it is deleted. After that it is too late to negotiate.
Have you verified with the cloud provider that your data is strictly logically segregated from other tenants?
Several customers share the same infrastructure. You have to make sure that your data is logically separated.
Are privileged cloud administrator accounts protected with multi-factor authentication?
A compromised administrator account opens the whole cloud environment. Multi-factor authentication is the simplest effective barrier.
08: What you get
Certificate, badge, verification page and evaluation
What you receive after passing the assessment, and what you use it for.
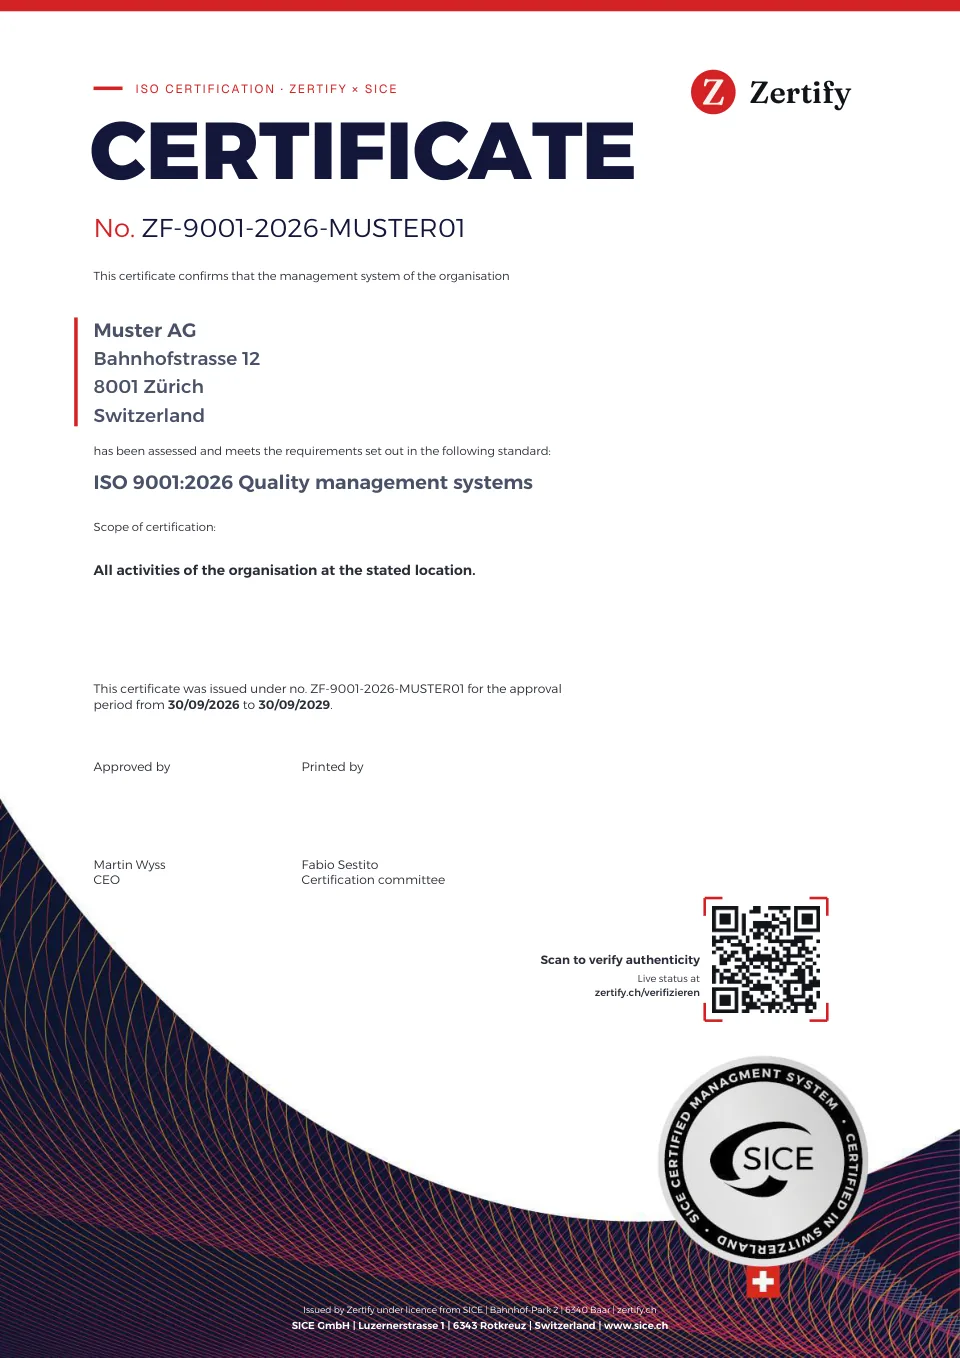
- Certificate as PDFWith number, QR code and the SICE seal. Valid for three years, confirmed by the yearly online re-audit. For customer enquiries, offers and supplier questionnaires.
- Badge for website and documentsFor your website, offers and email signature. One click leads to the verification page; on the website it always shows the current status.
- Public verification pageBy number or QR code, customers see for themselves which company and standard the certificate covers and whether it is valid.
- Evaluation of your assessmentShows which requirements you meet according to your answers and where you should improve.
- Customer accountCertificates, invoices, re-audit and add-ons in one place.
For ISO 27017, the certificate also shows the version of your Statement of Applicability (SoA). An SoA template is available as an add-on.
09: Price
Price and validity
First-year price
CHF 799
ISO 27017 is certified together with ISO 27001. The price is for ISO 27017, ISO 27001 is added. From 2 standards, 20% off applies.
- From year 2
- CHF 529 per year
- Validity
- 3 years
Your customer requires an audit or an accredited certification? Clarify requirements
Included in the price
- Online assessment with 34 questions
- Certificate as PDF, issued under licence from SICE
- Yearly online re-audit
- Support by email
The verification page shows the status, standard and validity of every certificate. Read more in the FAQ
See the sample and assessment method10: Editions
ISO 27017:2026 and ISO 27017:2015
ISO 27017:2026
Published on 27/07/2026.
In preparation at Zertify: the SICE Certification Board is reviewing the new question catalog. After that, you can choose this edition when you start the assessment.
What changes
- Second edition, published in July 2026. It replaces ISO/IEC 27017:2015, which has been withdrawn.
- The guidance is now built on ISO/IEC 27002:2022 and follows its four themes: organizational, people, physical and technological controls, including their attributes.
- Four cloud specific controls supplement the 93 controls of ISO/IEC 27002:2022: shared roles and responsibilities, agreement with cloud service partners, segregation in virtual computing environments, and detection and prevention of unauthorized use of cloud services.
- Some controls of the 2015 edition were merged or removed. A new Annex A maps the 2026 edition to the 2015 edition.
- A new Annex B covers the monitoring of cloud services.
ISO 27017:2015
New certificates are issued to this edition until ISO 27017:2026 is released.
There is no binding deadline yet for moving existing certificates. We will let you know once it is set.
11: Cost
What does ISO 27017 cost? Audit, consulting or self-assessment
ISO 27017 is usually not audited on its own but together with ISO 27001. The figures below therefore describe the surcharge for a company with 10 to 50 employees.
| Route | Indicative range | What is behind it |
|---|---|---|
| Accredited audit | Indicative rangeAs an extension of ISO 27001, CHF 2,000 to 5,000 on top | What is behind itThe extra cost comes from additional audit days for the cloud controls. Without an existing ISO 27001 certification, its cost is added. |
| Consulting and implementation | Indicative rangeCHF 5,000 to 15,000 one-off | What is behind itClarifying shared responsibility, hardening standard and logging. The effort is smaller when an ISMS already exists. |
| Zertify self-assessment | Indicative rangeCHF 799 in year 1, then CHF 529 per year | What is behind itYou check whether shared responsibility, return of data, tenant separation and administrator access are demonstrably settled. It does not replace ISO 27001 certification. |
All amounts are non-binding indicative ranges for Swiss SMEs, not quotes. The offers of the individual providers are what counts.
12: Duration
How long does ISO 27017 take?
If you already run an ISMS, you add ISO 27017 in a few months. Without an ISMS, the route starts at ISO 27001.
| Phase | Accredited | Zertify |
|---|---|---|
| Add cloud controls | Accredited2 to 4 months with an existing ISMS, otherwise 9 to 12 months including ISO 27001 | ZertifyNone. You rate the current state of your cloud use |
| Assessment | AccreditedExtra audit days within the ISO 27001 audit, samples from cloud configuration | ZertifyAbout 20 to 30 minutes online, scored immediately |
| Certificate | AccreditedRelease after 2 to 6 weeks, valid within the ISO 27001 certification cycle | ZertifyPDF with QR verification within 4 hours |
13: Further questions
Further questions about ISO 27017
Questions
Checklist
ISO 27017:2015 checklist by email
All 34 questions of the ISO 27017 self-assessment as a PDF to tick off, ordered by topic. Free, by email.
14: More standards
More standards
Many companies combine several standards. Two or more earn a discount.
- ISO 27001:2022: View standard
Information Security Management
ISO 27017 builds on the ISMS. Without risk analysis, SoA and audits the foundation is missing.
from CHF 849
- ISO 27018:2025: View standard
Cloud Privacy
If the cloud holds personal data, ISO 27018 adds data protection duties such as purpose limitation and deletion to the technical controls.
from CHF 799
15: Blog
Latest articles on ISO 27017
16: Questions
Frequently asked questions about ISO 27017
To both. The standard contains guidance for providers and for customers and describes the roles separately. The questions in the assessment mainly take the cloud user's view. The framework for both roles is ISO 27001, which is always part of it at Zertify.
At Zertify, yes. ISO 27017 adds cloud controls to an ISO 27001 ISMS, so we certify both together. If you choose ISO 27017, ISO 27001 is included in the assessment automatically, with a 20 % multi-standard discount. If you already hold a valid ISO 27001 certificate from Zertify, it is not needed again.
The provider secures the data centre, hardware and usually the platform. You secure configuration, access, data and users. The deeper you enter the stack, for example with IaaS, the more lies with you. The standard requires the split to be written down and known.
It is meant for cloud services, whether public, private or hybrid. For a classic data centre without tenants and self-service, many controls do not apply, and ISO 27001 is enough.
There are seven cloud specific additional controls: shared roles, return of assets, segregation in virtual environments, hardening of virtual machines, administrator operations, monitoring of cloud services and alignment of virtual and physical networks.
For proposals, supplier questionnaires, many tenders and internal use. It shows that you answered the requirements of the standard in the online assessment and that a member of the SICE Certification Board reviewed your answers. If a tender explicitly requires an accredited certificate, check this first via the Clarify requirements page.
ISO 27017 certificate within 4 hours.
The assessment is free. You pay only once you have passed.
The verification page shows the status, standard and validity of every certificate.