ISO 20000-1:2018
Apply for ISO 20000-1 online.
ISO 20000-1:2018 IT Service Management
Make it traceable how you manage service quality, incidents and changes in your IT services. You complete the self-assessment online, with no on-site audit. A member of the SICE Certification Board reviews your answers before the certificate is issued.
CHF 799 in the first year, then CHF 529 per year with an online re-audit.
Pricing- Questions
- 36
- Must-meet questions
- all 13
- Other questions
- min. 16 of 23
- Validity
- 3 years
- First-year price
- CHF 799
- From year 2
- CHF 529 per year
- Assessment time
- about 30 minutes
- Certificate after payment
- usually within 4 h
- Official standard
- iso.org
01: Overview
What is ISO 20000-1?
ISO 20000-1:2018 sets requirements for a service management system (SMS) for IT services. It builds on ITIL practices but, unlike ITIL, is certifiable. Requirements include a service catalogue, agreed service levels, incident, problem and change management, and continual improvement of the services.
02: Benefits
What ISO 20000-1 brings your business
The benefits of the standard come from an effectively implemented management system, not from the certificate alone. The Zertify certificate documents your reviewed answers.
- Service levels that are measured and reviewed with customers
- Fewer recurring outages through problem management
- Planned changes with approval and a rollback plan
- IT performance and cost made visible to business units
- A clear service catalogue instead of ad hoc requests
- Answers to service management questions in tenders for operations, hosting and helpdesk
03: Who it is for
Who is ISO 20000-1 for?
- IT service providers and managed service providers
- Internal IT departments
- Cloud service providers
- Data centres
- Software-as-a-service providers
- IT consulting firms
04: Requirements
Key requirements
Define the service portfolio and catalogue
Establish service level agreements (SLAs)
Set up incident and problem management
Implement change and release management
Operate capacity and availability management
Ensure continual service improvement
05: Demand
Who asks for ISO 20000-1?
ISO 20000-1 is asked for when IT is sold as a service and customers want to check that operations are dependable.
- Customers of managed service providers
- Banks, hospitals and industrial firms outsource operations and support and want proof that incident, change and service levels are under control.
- IT operations tenders
- For operations, hosting and help desk, ISO 20000-1 is a typical suitability criterion, sometimes together with ISO 27001.
- Internal IT and group companies
- Internal IT departments use the standard to make performance and costs transparent towards the business units.
06: Assessment
How the assessment works
The assessment has 36 yes/no questions, online and at your own pace. 13 of them are must-meet questions of our assessment and must all be answered yes. Of the other 23 questions you need at least 16 yes.
| The questions fall into these topics: | Questions | Mandatory |
|---|---|---|
| Context of the organization | 4 questions | 1 |
| Leadership | 5 questions | 1 |
| Planning | 4 questions | 2 |
| Support | 6 questions | 1 |
| Operation | 11 questions | 5 |
| Performance evaluation | 3 questions | 2 |
| Improvement | 3 questions | 1 |
After the assessment, a member of the SICE Certification Board reviews your answers. Only then does Zertify issue the certificate.
07: Sample questions
Sample questions from the ISO 20000-1 assessment
Four of 36 questions from the catalogue, and why they count.
Are service requirements defined?
Without defined service requirements nobody knows what a service is measured against. They are the basis of every service level.
Is there a service level management process?
Service levels make performance measurable and contractually binding. Auditors check whether the figures are actually collected and discussed.
Is there a problem management process?
Incident management fixes symptoms, problem management the cause. Those who separate the two see recurring disruptions fall.
Are changes carried out in a controlled manner?
Many major outages are the result of badly planned changes. Approval and a rollback plan are the core of change management.
08: What you get
Certificate, badge, verification page and evaluation
What you receive after passing the assessment, and what you use it for.
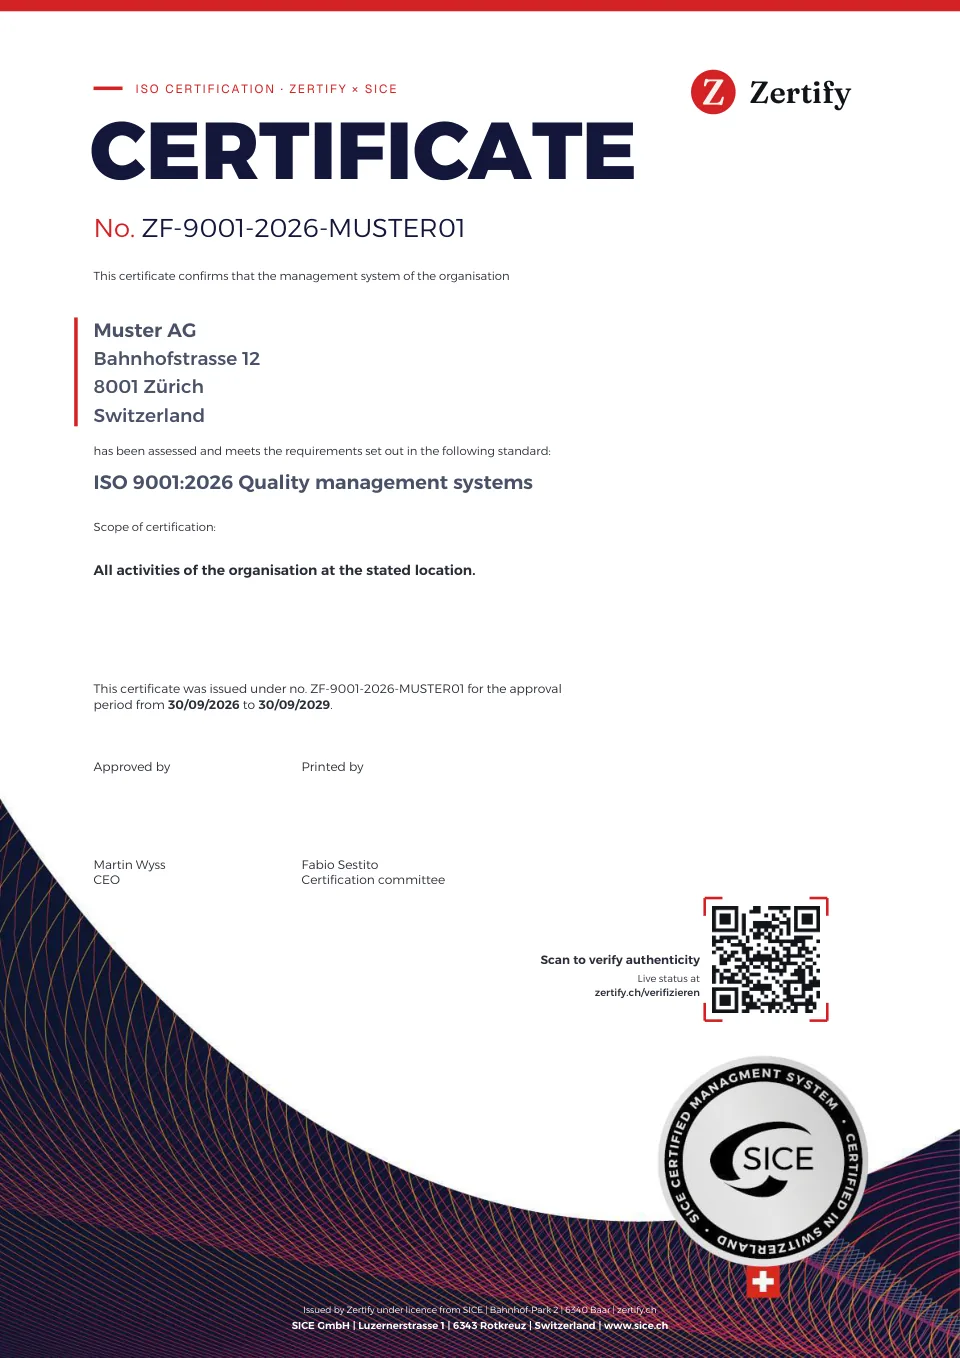
- Certificate as PDFWith number, QR code and the SICE seal. Valid for three years, confirmed by the yearly online re-audit. For customer enquiries, offers and supplier questionnaires.
- Badge for website and documentsFor your website, offers and email signature. One click leads to the verification page; on the website it always shows the current status.
- Public verification pageBy number or QR code, customers see for themselves which company and standard the certificate covers and whether it is valid.
- Evaluation of your assessmentShows which requirements you meet according to your answers and where you should improve.
- Customer accountCertificates, invoices, re-audit and add-ons in one place.
09: Price
Price and validity
First-year price
CHF 799
- From year 2
- CHF 529 per year
- Validity
- 3 years
Your customer requires an audit or an accredited certification? Clarify requirements
Included in the price
- Online assessment with 36 questions
- Certificate as PDF, issued under licence from SICE
- Yearly online re-audit
- Support by email
The verification page shows the status, standard and validity of every certificate. Read more in the FAQ
See the sample and assessment method10: Cost
What does ISO 20000-1 cost? Audit, consulting or self-assessment
With ISO 20000-1 the number and complexity of services drive the price. For an IT provider with 10 to 50 employees, these orders of magnitude apply.
| Route | Indicative range | What is behind it |
|---|---|---|
| Accredited audit | Indicative rangeCHF 10,000 to 25,000 initial audit, then 5,000 to 10,000 per year | What is behind itAudit days depend on the number of services, sites and people in scope. A narrow service catalog keeps the price low. |
| Consulting and implementation | Indicative rangeCHF 20,000 to 60,000 one-off | What is behind itBuilding a service catalog, service levels, incident, problem and change processes, plus adapting tools. The processes have to be lived, not just exist. |
| Zertify self-assessment | Indicative rangeCHF 799 in year 1, then CHF 529 per year | What is behind itYou check whether service catalog, service levels, incident, problem and change management demonstrably run. It does not replace an auditor's sampling in your ticket system. |
All amounts are non-binding indicative ranges for Swiss SMEs, not quotes. The offers of the individual providers are what counts.
11: Duration
How long does ISO 20000-1 take?
An accredited ISO 20000-1 process usually takes nine to eighteen months, because processes first have to generate evidence over several weeks.
| Phase | Accredited | Zertify |
|---|---|---|
| Build processes | Accredited6 to 12 months for service catalog, service levels and processes, then several months of operating evidence | ZertifyNone. You rate the current state of your services |
| Assessment | AccreditedStage 1 (documents) and stage 2 (samples from tickets and changes) | ZertifyAbout 20 to 30 minutes online, scored immediately |
| Certificate | AccreditedRelease after 2 to 6 weeks, then annual surveillance audits | ZertifyPDF with QR verification within 4 hours |
12: Further questions
Further questions about ISO 20000-1
Questions
Checklist
ISO 20000-1:2018 checklist by email
All 36 questions of the ISO 20000-1 self-assessment as a PDF to tick off, ordered by topic. Free, by email.
13: More standards
More standards
Many companies combine several standards. Two or more earn a discount.
- ISO 27001:2022: View standard
Information Security Management
IT providers are often asked about service quality and security together, and incident and change are central in both standards.
from CHF 849
- ISO 9001:2026: View standard
Quality Management
If you run services to ISO 20000-1, you can use the same audit and improvement processes for quality across the whole company.
from CHF 599
14: Blog
Latest articles on ISO 20000-1
15: Questions
Frequently asked questions about ISO 20000-1
ITIL is a framework of good practice that no organisation can be certified against. ISO 20000-1 sets auditable requirements against which organisations are certified. If you use ITIL, you already meet many of these requirements.
Yes, if IT has to prove its performance to the business units. You get defined services, service levels and indicators. Externally the benefit shows mainly at corporations and regulated businesses.
ISO 27001 protects information, meaning confidentiality, integrity and availability. ISO 20000-1 secures the quality of services. Both use the same structure, overlap on incident and change, and are often combined.
The scope names the services, organisational units and locations the system covers. It may be narrow, but it must not be chosen to hide weak spots. Customers read the scope on a certificate first.
ISO 20000-1:2018 follows the High Level Structure and additionally requires risk and knowledge management. Process specifications were simplified and requirements for leadership and objectives strengthened. The 2011 edition is superseded.
For proposals, supplier questionnaires, many tenders and internal use. It shows that you answered the requirements of the standard in the online assessment and that a member of the SICE Certification Board reviewed your answers. If a tender explicitly requires an accredited certificate, check this first via the Clarify requirements page.
ISO 20000-1 certificate within 4 hours.
The assessment is free. You pay only once you have passed.
The verification page shows the status, standard and validity of every certificate.